
Section
Latest
Every story, newest first.
-
Outage
Major U.S. Bank Outage: Chase Technical Failure Disrupts Transactions and Zelle Payments
A software bug in an on-premises hardware system at JPMorgan Chase delayed transactions on November 16, 2026. Chase says it was not a cyberattack, and Zelle says its network stayed up.
-
Patch
Grype v0.122.0 fixes all-layers scan gaps and other matching bugs
Grype v0.122.0 makes --scope all-layers scans report packages removed in a later layer, fixes RPM caret version sorting and CVSS parsing, and bumps OpenTelemetry to v1.47.0 for GHSA-q7gw-24fr-5p69. Update Grype to v0.122.0.
-
Security tools
BloodHound CE v9.10.0 fixes CVE-2026-16221 and tightens domain permissions
BloodHound CE v9.10.0 fixes CVE-2026-16221, though the release notes give no description or severity score, and now requires graph write permission on the domain PATCH endpoint. Self-hosters should update and switch Findings integrations from zoneid to assetgrouptagid.
-
Self-hosted
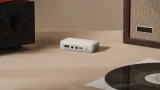
Home Assistant Connect AUX-2 adds audio, serial and Bluetooth hub
Nabu Casa launched the Home Assistant Connect AUX-2, a small box that streams audio, controls RS-232 serial devices, hosts a Z-Wave adapter and acts as a Bluetooth hub. It suits older amplifiers and legacy gear. On sale worldwide from 2026-11-11 at $69 / €59.
-
Prompt Shift
Google Maps' "Ask Maps" adds trip itineraries and appointment finding
Google added itinerary building, saved-list search, "Know before you go" route tips and appointment finding to Gemini-powered Ask Maps on Android and iOS. Route tips and appointments launch first in the U.S.; appointment finding is opt-in and can call businesses for you.
-
Release
Tailscale v1.104.7 released; GitHub notes point to the changelog
Tailscale has released v1.104.7 on GitHub, but its release notes only point to the Tailscale changelog, so the changes are unknown. Users should read the changelog entry first, then test the update on one node before wider rollout.
-
Under the Hood
Tailcat vs Tailscale: same data plane, no control plane
Tailcat, an open-source Go package and netcat-style CLI, carries bytes over Tailscale's data plane (WireGuard, NAT traversal, DERP) with no control plane or accounts. It suits quick two-machine links; Tailscale suits auditable access. Run your own relay for privacy.
-
Vulnerability
High
Gitea 28.3.0 fixes RubyGems index poisoning flaw (CVE-2026-118389)
Gitea 28.3.0 fixes a high-severity RubyGems flaw (CVSS 8.1) where newlines in package metadata let attackers forge index entries, so bundler can install a malicious gem. Instances hosting RubyGems packages on 28.2.0 or earlier should update to 28.3.0.
-
Release
Docker Engine 29.10.0 changes how loopback registries are treated as insecure
Docker Engine 29.10.0 no longer treats loopback addresses as insecure when insecure-registries or --insecure-registry is set, so local registry pulls and pushes may fail. Use trusted TLS or list addresses like localhost:5000 before upgrading.
-
Patch
Medium
Ubuntu USN-9064-2 fixes Pillow resize regression and code-execution flaws
Ubuntu's USN-9064-2 fixes a Pillow regression where the USN-9064-1 patch for CVE-2026-112402 broke NEAREST-filter resizing and mode 1 or P image resizing. It also carries code-execution fixes such as CVE-2026-112393. Install the updated package and check your release's advisory.
-
Security tools
OpenCTI 7.261116.0 adds password reuse blocking and STIX export fixes
OpenCTI 7.261116.0 blocks reuse of old passwords, adds System asset fields, and fixes STIX 2.1 export dropping 0 latitude or longitude values and alias loss. STIX 2.1 exporters should update; the truncated release notes reviewed give no upgrade steps.
-
AI
LiteLLM v1.108.9 backports Bedrock, Azure and Vertex AI fixes to LTS
LiteLLM v1.108.9 backports fixes to the lts/1.108.x branch for Responses, Bedrock, Azure AI, Vertex AI and Vercel AI Gateway. LTS users of those providers should check the list against their setup, then verify the cosign image signature before upgrading.
-
Outage
Microsoft 365 outage was a technical fault, not an attack, Microsoft says
Microsoft says the November 12 Microsoft 365 outage, which disrupted Exchange Online and Outlook, was a technical fault, not a cyberattack. Phishers then abused incident ID EX1550543. Admins should verify outage notices in the admin center before trusting them.
-
Vulnerability
High
OpenCTI 7.260811.0 fixes template sandbox escape that gives server code execution
OpenCTI 7.260811.0 fixes a safeEjs template verifier bypass: a crafted regex literal lets authenticated users with certain capabilities run JavaScript on the server, scored 8.8 (High). Update to 7.260811.0, or LTS 7.260309.0-lts.7 or later.
-
Security tools
Teleport 18.11.10 patch: stricter phase.yaml shell errors, Beam audit replay
Teleport 18.11.10 makes multi-line shell commands in phase.yaml fail on the first error, adds replay of Beam audit events, and fixes MCP tool-list responses that dropped fields. Review phase.yaml files before updating.
-
Vulnerability
High
Suricata 8.0.8 fixes HTTP/2, SIP and FTP denial-of-service flaws
Suricata 8.0.8 fixes a batch of advisories, including high-severity denial-of-service flaws scored CVSS 7.5 in FTP, HTTP/2 and SIP handling. Anyone running Suricata 8.0.x before 8.0.8 should update every install to 8.0.8.
-
Self-hosted
Grafana Pyroscope adds Python and Rust memory profiling, .NET Windows preview
Grafana Pyroscope's Python and Rust SDKs now support memory profiling, and .NET profiling on Windows x64 is in public preview. Exemplars need the v2 storage layer, and Windows .NET needs profiler version 1.3.0 or later.
-
Vulnerability
High
Gitea 28.4.0 fixes authenticated code execution and other flaws
Gitea 28.4.0 fixes security flaws in 28.3.0 and earlier, including CVE-2026-125423, which lets a signed-in user run commands as the Gitea OS account, and CVE-2026-123006 (CVSS 8.8), which exposes password hashes. Update to 28.4.0.
-
Daily brief
Daily brief: Monday 16 November 2026
11 published.
-
Under the Hood
CrowdSec bouncers vs Fail2Ban regex parsing: how each one blocks attackers
CrowdSec detects attackers with behavior-based scenarios and blocks them through bouncers, while Fail2Ban matches regex filters in jails and runs firewall actions. Fail2Ban suits a single box, CrowdSec several machines. Test a ban from a spare address first.
-
Weekend Build
Build a pull-based off-site copy of your Proxmox backups in one afternoon
An off-site Proxmox Backup Server can pull an on-site datastore on a schedule through a sync job, with its own prune retention. It targets losing every copy at once. Immutability and the restore drill are left to you.
-
Weekend Build
Put Proxmox admin sign-in behind Pocket ID passkeys and a management-only firewall
A weekend build puts Proxmox VE admin sign-in behind a Pocket ID OpenID Connect realm and turns on the default-off Proxmox firewall, limiting web GUI port 8006 to a management IP list. Keep a PAM admin and an open SSH session as fallback.
-
Friday Footgun
Traefik: close api.insecure and put the dashboard behind authentication
Traefik's api.insecure option exposes the API and dashboard, including sensitive configuration data, on the traefik entryPoint. Check your files, set it to false, and put the dashboard behind a basicAuth middleware with hashed passwords, keeping the API port off public networks.
-
Deep Dive
Opinion
Caddy and NGINX on a public port: why family apps belong behind an overlay
Ping2Prompt's position: family apps should skip a public reverse proxy and use an overlay network or outbound tunnel. Tailscale Serve keeps a port tailnet-only, and Cloudflare Tunnel lets you block inbound traffic. Public ports stay a reviewed exception.


Newsletter
Get the Weekly Brief
What happened, why it matters and what comes next: the week in one email, every Sunday morning.
Free. One email, Sunday morning. What you get