
Section
Self-hosted
The apps you run yourself: new releases, breaking changes, migrations and security fixes.
-
Vulnerability
High
Portainer fixes Git credential leak to read-only users in 2.45.4 and 2.39.9
Portainer 2.45.4 and 2.39.9 fix a flaw letting read-only users send a shared Git source's stored username and password or token to a host they choose. Update to 2.45.4, 2.39.9 or 3.0.0 or later.
-
Vulnerability
High
Portainer 2.45.4 fixes network access bypass for Standard Users
Portainer skipped network resource control when workloads were created on a named network, letting Standard Users join other teams' private Docker networks if they know the name or ID. Update to 2.45.4, 2.39.9 or 3.1.0.
-
Self-hosted
Portainer 2.39.9 LTS fixes Critical Go flaws and access-control bypasses
Portainer 2.39.9 LTS fixes Critical Go flaws CVE-2026-56857 and CVE-2026-78663 plus several access-control bypasses. It also stops trusting eMudhra certificates, which can break SSO, LDAPS and Git connections. Update to 2.39.9 after checking certificates and stacks.
-
Vulnerability
High
Music Assistant 2.8.0 fixes authenticated Python code execution (CVE-2026-73971)
Music Assistant 2.8.0 fixes CVE-2026-73971, a CVSS 8.0 flaw letting any authenticated user run arbitrary Python code with server privileges in versions before 2.8.0. Default installs are exposed, so update to 2.8.0; no workaround is given.
-
Patch
Critical
nginx 1.30.7 and 1.31.9 fix ten vulnerabilities, upgrade now
nginx released stable 1.30.7 and mainline 1.31.9 on 2026-11-18, fixing ten CVEs across the resolver, HTTP/2, HTTP/3, mail proxy and stream modules. Exploitation status is unknown. Upgrade stable installs to 1.30.7 and mainline installs to 1.31.9.
-
Vulnerability
Medium
NetBird dashboard 2.96.0 fixes browser RDP certificate warning bypass
NetBird's browser RDP client warns about an untrusted certificate only once per page session, so a substitute endpoint can collect RDP credentials. Dashboard 2.19.0 through 2.95.x is affected (Medium, CVSS 4.0 score 5.9); update to 2.96.0.
-
Vulnerability
High
NetBird v0.80.0 fixes local root escalation in install.sh
NetBird's install.sh, in v0.79.0 and earlier, stages downloads in guessable /tmp paths, letting a local unprivileged user gain root during install or update, mostly on macOS. Update to v0.80.0 and use its script; v0.79.0 is not fixed.
-
Patch
Aeotec joins Works with Home Assistant with nine certified devices
Aeotec joined Works with Home Assistant with nine certified devices, five of them Z-Wave Long Range. Certified devices run locally without the cloud. Long Range needs an adapter such as the Home Assistant Connect ZWA-2; older adapters work without the extra reach.
-
Vulnerability
High
DeepAudit SSRF flaw leaks GitLab and Gitea tokens; no fix yet
CVE-2026-129880, a high-severity (8.3) SSRF flaw in DeepAudit 2.0.0-beta.5 through 3.8.0, lets any registered user leak the server-wide GitLab or Gitea token. No fix is published yet; limit who holds accounts and rotate the token.
-
Vulnerability
High
NetBird 0.80.0 fixes Windows service accounts treated as administrators
NetBird 0.80.0 fixes a Windows daemon flaw that treated LOCAL SERVICE and NETWORK SERVICE accounts as administrators, letting a compromised process change privileged settings. Versions 0.76.0 up to 0.80.0 are affected; upgrade to 0.80.0.
-
Self-hosted
n8n 2.48.5 is now stable, with AI Agent and credential fixes
n8n 2.48.5, dated 2026-11-18, is now the stable release. It mostly fixes AI Agent tool-call history and streaming, team project credential checks, and the Microsoft Teams Trigger and Qdrant nodes. A normal update window fits; nothing reads as urgent.
-
Patch
High
Uptime Kuma 2.5.12 sandboxes a dangerous library in security fixes
Uptime Kuma 2.5.12 sandboxes a library its release notes call dangerous (PR #8187) and updates a dependency (PR #8167). The notes name no library, affected range or exploitation status. Users on older releases should update to 2.5.12 and back up first.
-
Patch
High
Audiobookshelf 2.38.0 closes access-control gaps and server crashes
Audiobookshelf v2.38.0 fixes server crashes and access-control gaps, including non-admin users reaching another user's playback session and empty tag allow lists granting full access. Multi-user servers on v2.37.2 or earlier should update to v2.38.0.
-
Vulnerability
Critical
Pi-hole FTL 6.7 fixes five flaws, including a critical 9.2 flood bug
Pi-hole FTL 6.7 fixes five flaws, led by CVE-2025-62165 (9.2, critical), where unauthenticated clients can flood the WebUI login page and API, which can make the WebUI sluggish or unresponsive. Upgrade to FTL 6.7; no other workaround is stated.
-
Self-hosted
Grafana Cloud Logs full-text search is now generally available
Full-text search is now generally available in Grafana Cloud Logs, adding a secondary index to Loki. Grafana says it finds specific log lines across weeks without a full scan, with no pipeline changes. Try it in Explore with a line filter.
-
Vulnerability
High
Pocket ID v2.19.3 fixes OAuth device approval flaw that enables account takeover
Pocket ID v2.19.3 fixes a high-severity flaw (CVSS 8.1) where a crafted link silently approves an attacker's OAuth device grant, enabling account takeover at connected services. Versions up to v2.19.2 are affected; update to v2.19.3.
-
Self-hosted
Paperless-ngx 3.5.0 adds manual workflow triggers and async bulk operations
Paperless-ngx 3.5.0 adds manual workflow triggers, markdown document notes and async bulk operations, plus permission, OCR and PostgreSQL workflow fixes. Nothing is marked breaking, so update on your usual schedule; prioritise it with PostgreSQL scheduled workflows.
-
Vulnerability
Medium
Gitea 28.4.0 linked to fix for fork web editor branch read flaw
Gitea's fork web editor could copy branches from the base repository without checking read access (CVE-2026-123009, CVSS 4.3). Users who lost access could still read current branches. Update to Gitea 28.4.0 and confirm the fix in advisory GHSA-9vh6-6hgj-j5m5.
-
Vulnerability
High
Gitea fixes unlimited TOTP guessing that weakens two-factor sign-in (CVE-2026-123002)
Gitea now refuses an account's two-factor (TOTP) attempts for 15 minutes after five wrong codes, fixing a 7.5 HIGH flaw that allowed unlimited guessing by attackers who know the password. Users with two-factor enabled should update to v28.4.0, which the record references.
-
Self-hosted
Home Assistant 2026.11.2 patch release fixes many integrations
Home Assistant 2026.11.2 is a patch release fixing bugs across many integrations, including UniFi, Hue, Reolink and MQTT, and bumping aioftp to 0.28.3 as a security item. Yi users should update; inputtext.setvalue now rejects values violating its pattern.
-
Self-hosted
Home Assistant Connect AUX-2 adds audio, serial and Bluetooth hub
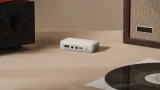
Nabu Casa launched the Home Assistant Connect AUX-2, a small box that streams audio, controls RS-232 serial devices, hosts a Z-Wave adapter and acts as a Bluetooth hub. It suits older amplifiers and legacy gear. On sale worldwide from 2026-11-11 at $69 / €59.
-
Vulnerability
High
Gitea 28.3.0 fixes RubyGems index poisoning flaw (CVE-2026-118389)
Gitea 28.3.0 fixes a high-severity RubyGems flaw (CVSS 8.1) where newlines in package metadata let attackers forge index entries, so bundler can install a malicious gem. Instances hosting RubyGems packages on 28.2.0 or earlier should update to 28.3.0.
-
Self-hosted
Grafana Pyroscope adds Python and Rust memory profiling, .NET Windows preview
Grafana Pyroscope's Python and Rust SDKs now support memory profiling, and .NET profiling on Windows x64 is in public preview. Exemplars need the v2 storage layer, and Windows .NET needs profiler version 1.3.0 or later.
-
Vulnerability
High
Gitea 28.4.0 fixes authenticated code execution and other flaws
Gitea 28.4.0 fixes security flaws in 28.3.0 and earlier, including CVE-2026-125423, which lets a signed-in user run commands as the Gitea OS account, and CVE-2026-123006 (CVSS 8.8), which exposes password hashes. Update to 28.4.0.


Newsletter
Get the Weekly Brief
What happened, why it matters and what comes next: the week in one email, every Sunday morning.
Free. One email, Sunday morning. What you get